Skip to content
CMMC Consulting
Strategic Guidance to Help Your Organization Achieve CMMC Compliance
All contractors and subcontractors in the U.S. Defense Industrial Base (DIB) are required to comply with Cybersecurity Maturity Model Certification (CMMC). This multilevel security framework protects sensitive government information from cyber breaches and threats to national security within the defense supply chain.
NVS guides organizations on their way to CMMC certification. Our CMMC compliance support is tailored to your needs, helping you determine each step required for certification.
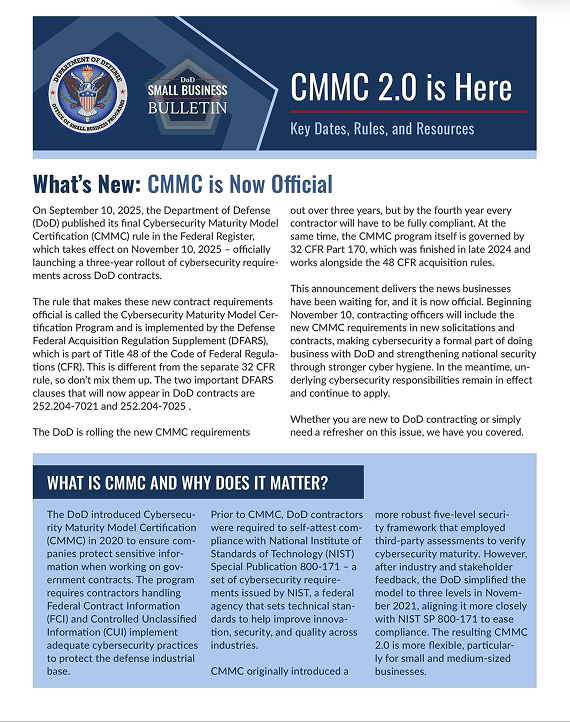
About Cybersecurity Maturity Model Certification (CMMC) 2.0
The U.S. Department of Defense (DoD) has been working to improve cybersecurity within the DIB. The CMMC is a DoD program that ensures contractors and subcontractors can safeguard Federal Contract Information (FCI) and Controlled Unclassified Information (CUI).
The CMMC Final Rule, also called CMMC 2.0, was published on October 15, 2024. Its goal is to protect sensitive data shared with defense contractors and subcontractors before, during, and after projects are completed. CMMC 2.0 streamlines requirements and aligns with existing and widely accepted cybersecurity standards, including the National Institute of Standards and Technology (NIST SP 800-171).
The CMMC Final Rule has three primary features:
Tier levels: The CMMC program defines three advanced levels. Based on the sensitivity of the managed information and data, organizations must implement advanced cybersecurity standards.
Assessments: Organizations must meet compliance standards within their selected CMMC level. A company must attest to its compliance status and will likely need to organize third-party assessments.
Contracts: An organization’s contract will outline its certification requirements.
NVS focuses on providing the required expertise to streamline your path to CMMC certification. Often after a quick introductory call with our team, you can identify any critical challenges that would impact your organization’s ability to reach its certification goals.
CMMC Advisory and Compliance Services
CMMC compliance is now a contractual requirement for organizations that support the Department of Defense supply chain. NVS Strategic Solutions provides structured CMMC advisory and compliance support to help organizations meet requirements, reduce risk, and remain competitive for DoD and prime contractor opportunities.
Our CMMC services are designed to be practical and execution-focused. We work alongside your team to interpret requirements, define scope accurately, and build a compliance roadmap that aligns with how your organization actually operates—without unnecessary complexity or overengineering.
CMMC Compliance Strategy and Readiness
We begin with a comprehensive CMMC compliance strategy tailored to your contract requirements, data environment, and business model. Each engagement includes dedicated advisory support to help you understand evolving requirements, identify risks early, and plan remediation activities in a controlled and measurable way.
Our goal is to position your organization for compliance without disrupting operations or introducing avoidable cost.
CMMC Security Assessment and Scoping
A critical component of CMMC success is defining scope correctly. We assess how Controlled Unclassified Information (CUI) flows into, within, and out of your organization to determine the appropriate compliance boundary for your System Security Plan (SSP).
Once scope is established, we conduct a structured risk assessment to identify gaps and vulnerabilities against CMMC-aligned controls, prioritizing remediation efforts based on impact and certification readiness.
CUI Identification and Management
We assist organizations in identifying and managing both basic and specified forms of CUI, including data subject to additional handling requirements such as ITAR.
Our advisory support focuses on establishing clear handling procedures, access controls, and documentation that align with CMMC expectations while supporting day-to-day operations. Proper CUI identification and management reduces audit risk and prevents unnecessary expansion of compliance scope.
CMMC Gap Analysis
We evaluate your existing cybersecurity posture against applicable CMMC requirements to identify gaps that must be addressed prior to certification. This assessment provides a clear, prioritized view of where controls, processes, or documentation need improvement.
The result is a practical readiness snapshot that informs your remediation plan and supports leadership decision-making.
Implementation and Remediation Support
NVS provides hands-on support to help implement required controls, policies, and procedures. This may include strengthening existing safeguards, formalizing processes, or introducing new security measures where necessary.
We ensure controls are not only implemented, but operationalized—producing the evidence required to demonstrate compliance during a C3PAO assessment.
Documentation Development and Support
CMMC requires detailed and accurate documentation. We support the development and maintenance of required artifacts, including System Security Plans, Risk Assessments, policies, incident response documentation, and related procedures.
Where gaps remain, we assist with developing Plans of Action and Milestones (POA&Ms) that clearly document remediation efforts and timelines in alignment with CMMC expectations.
Certification Readiness and Audit Support
Prior to your C3PAO assessment, we conduct a CMMC readiness review to validate that controls are implemented, documentation is complete, and evidence is available. This step helps reduce surprises and strengthens audit preparedness.
When appropriate, we support organizations during the certification process to help manage questions, clarify documentation, and ensure alignment between implemented controls and audit expectations.
Why Organizations Choose NVS for CMMC Support
CMMC requirements are being phased into DoD contracts over multiple years, making early preparation critical. Organizations engaging NVS benefit from a structured, business-aware approach to compliance that balances regulatory requirements with operational reality.
We work with organizations operating in regulated environments across defense-adjacent industries, helping them align existing cybersecurity programs with CMMC requirements to reduce timelines and avoid unnecessary duplication.
Our approach is tailored, transparent, and focused on long-term sustainability—not just passing an audit.